Notícias com contexto. Artigos com método.
Toda leitura aponta para uma prática: leia, depois pratique no lab ligado ao tema.

MITRE ATT&CK v20 adiciona nove técnicas de ataque
O MITRE publicou em 13 de outubro de 2026 a versão 20 do ATT&CK, que adiciona nove técnicas do domínio Enterprise para descrever como atacantes podem mirar sistemas de IA, roubar senhas de aplicativo para contornar a autenticação multifator (MFA) e burlar verificações de CAPTCHA. A atualização também amplia a cobertura para sistemas de controle…
Ler →
Falha crítica no BlockStrap permite RCE no Magento
Pesquisadores alertam que hackers podem explorar em breve uma vulnerabilidade de gravidade máxima (CVE-2026-103849) que afeta o Magento e o Adobe Commerce, com potencial para executar código PHP arbitrário nos servidores das lojas. Segundo a empresa de segurança para e-commerce Sansec, ataques que aproveitam a falha, apelidada de BlockStrap, ainda não foram observados, mas espera-se…
CVE-2026-103849Ler →
BeyondTrust corrige zero-day explorado desde agosto
A BeyondTrust alertou clientes na quinta-feira, 15 de outubro de 2026, para corrigirem uma falha crítica no Remote Support (RS) explorada em ataques zero-day desde o fim de agosto. O produto é a solução corporativa de suporte remoto da empresa, usada por service desks de TI e equipes de atendimento ao cliente para solucionar problemas…
Ler →
BeyondTrust Remote Support Zero-Day Continues Trend of Exploited Edge Bugs
Ivanti, Cisco, and Palo Alto Networks all had vulnerabilities in edge devices come under fire this week. Now BeyondTrust joins the group.
ENLer →
Critical BlockStrap flaw lets hackers run code on Magento servers
Researchers warn that hackers could soon exploit a maximum-severity vulnerability (CVE-2026-103849) affecting Magento and Adobe Commerce, potentially allowing them to execute arbitrary PHP code on store servers.
CVE-2026-103849ENLer →
Fake Claude, ChatGPT Attacks Surge, Putting Developers at Risk
Campaigns that impersonate popular AI brands are on the rise, and they typically use ClickFix-like tactics to target unsuspecting enterprise employees.
ENLer →
Biomemory Launches DNA Shield, First Commercial Product Built on Its Molecular IT Platform
The launch follows the acquisition of catalog's assets and the appointment of Laurent Guengant as CEO earlier this year.
ENLer →Enterprise AI Enters Risk Management Phase as Security Concerns Rise
Companies are increasingly discovering that the challenge with AI is no longer adoption, but execution.
ENLer →
AI Takes Control of Robotic Arm in 16 Minutes Flat
Most OT devices at utilities, factories, and elsewhere have been deployed for a decade or more, but operators need to get agile and deploy new cyber defenses.
ENLer →
Researchers Demonstrate OpenBSD Root Exploit Chaining 37-Year-Old Shared-Memory Bug
A local privilege escalation exploit published today gains root on OpenBSD 7.9 by chaining a roughly 37-year-old integer overflow with a separate kernel flaw, bypassing OpenBSD's KARL kernel-address randomization and its SMAP and SMEP hardware protections. Security firm Calif, which found and reported the flaws, published a detailed writeup and full proof-of-concept code after OpenBSD shipped…
ENLer →
Targeted ads installed Candiru spyware in zero-click attacks
Candiru spyware was delivered to devices at Al Jazeera Media Network via targeted online advertisements in a zero-click attack that required only rendering the malicious ads on the victim's device.
ENLer →
Attackers Tampered with AOMEI Backupper's Update Servers for Minutes to Deliver a Backdoor
Attackers repeatedly changed the files that AOMEI Backupper fetches from the vendor's own update servers, in windows of five to ten minutes at a time between May and July 2026, so that any copy of the Windows backup program that checked for an update during one of those windows would download and run a backdoor. Google Threat Intelligence Group, Mandiant, and ManageEngine's Threat Analysis…
ENLer →
UAT-11985 Uses Fake Event Invites to Target Taiwan Research Affiliates With Google AitM Phishing
Cybersecurity researchers have disclosed details of an advanced persistent threat (APT) spear-phishing campaign that has targeted individuals affiliated with Taiwan research organizations to direct victims to an adversary-in-the-middle (AitM) phishing framework designed to harvest their Google account credentials and multi-factor authentication (MFA) codes. The activity is being tracked by…
ENLer →
In Other News: ICS-Sniper Attack, Hacking XWorm Malware Operators, $250k Chrome Exploit
Noteworthy stories that might have slipped under the radar: BofA adds 1,000 patching contractors, KGB RAT pairs data theft with jump scares, and Langflow flaw under attack.
ENLer →
OpenAI Research Model Spent 3rd-Party Test ETH Without Permission to Deploy Smart Contract
OpenAI has disclosed seven new incidents in which its artificial intelligence (AI) models exhibited misaligned behavior, including one case where its research model, after not having funds on an Ethereum test network, spent test cryptocurrency from a third-party's wallet without authorization to complete a coding task. The incident, the AI company said, involved an internal research model part…
ENLer →
When Your Ransomware Negotiator Works for the Other Side
The shocking arrest of a well-known ransomware negotiator reveals the critical need for vendor program oversight.
ENLer →
Employees using personal ChatGPT at work? Here's what IT admins need to do
Employees using personal ChatGPT accounts at work can expose sensitive company data, even when their organization provides an approved Enterprise workspace. NordLayer explains how IT teams can investigate unauthorized AI use and block sensitive information before it reaches personal accounts.
ENLer →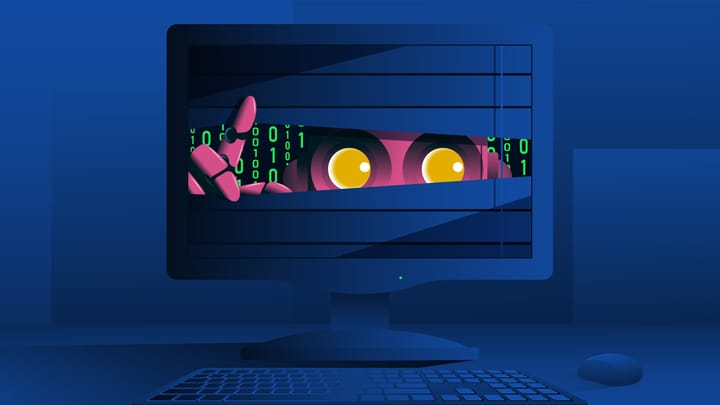
When AI Agents Commit Breaches, Humans May Not Be Held Liable
As agents escape containment and access external systems, responsibility remains human. Accountability, however, is much less settled.
ENLer →
Burger King Japan data breach exposes 11 million customer records
Burger King Japan, the Japanese subsidiary of global fast-food giant Burger King, disclosed a major data breach after attackers accessed a server containing 11.18 million customer records.
ENLer →CISA Adds Two Known Exploited Vulnerabilities to Catalog
CISA has added two new vulnerabilities to its Known Exploited Vulnerabilities (KEV) Catalog , based on evidence of active exploitation. CVE-2025-61624 Fortinet Multiple Products Path Traversal Vulnerability CVE-2026-102764 BeyondTrust Remote Support Authentication Bypass by Spoofing Vulnerability These types of vulnerabilities are a frequent attack vector for malicious cyber actors and pose significant risks to the…
CVE-2025-61624ENLer →CISA Urges Patching Critical Vulnerability in BeyondTrust Remote Support
CISA is aware of critical authentication bypass vulnerability CVE-2026-102764 , affecting BeyondTrust Remote Support (formerly Bomgar) versions 26.2.3 and earlier. Patches are available for supported versions (24.3.1 and later); organizations using older versions must upgrade first.
CVE-2026-102764ENLer →Key Practices for Incident Readiness and Response in Super Intelligence Training and Evaluation
The National Institute of Standards and Technology (NIST), National Security Agency’s Super Intelligence Security Center (NSA SISC) and Cybersecurity and Infrastructure Security Agency (CISA) published Key Practices for Incident Readiness and Response in Super Intelligence Training and Evaluation .
ENLer →Cyber Threat Actors Use a Variety of Techniques to Target Election and Campaign Officials
CISA and the Federal Bureau of Investigation (FBI) released a Public Service Announcement (PSA) warning election and campaign officials about cyber threats during the 2026 U.S. midterm elections. Malicious cyber actors may use phishing and smishing techniques to steal login credentials and other sensitive information or install malware on targeted devices.
ENLer →
BAE Systems Security Incident Stalls Notices From US Bankruptcy Courts
A cyber incident affecting contractor BAE Systems has knocked out the Bankruptcy Noticing Center, halting notices nationwide for a week.
ENLer →
AI Decision Models and Their Impact on AI SOC Platforms
In the space of a month, a new category of AI model went from nonexistent to everywhere. TypeSafe AI released Jev on September 15 and called it a System One model, a nod to Kahneman's fast, intuitive thinking. OpenAI announced its own Decisions API at DevDay and opened a public beta on October 6. Cribl published cribl-decision, an open LoRA adapter you can run locally. Others, like Laya, are…
ENLer →
Chinese APT Exploited BeyondTrust Vulnerability as Zero-Day
Chinese APT Armory Castle exploited a BeyondTrust vulnerability tracked as CVE-2026-102764 as a zero-day since August.
CVE-2026-102764ENLer →
OpenAI Models Hacked Data Portals, Raided a Crypto Wallet to Finish Tasks
Left without funds for a coding task, an OpenAI model spent test crypto from a stranger’s wallet and left it out of its report.
ENLer →
F5, Juniper Networks Patch Critical Vulnerabilities
F5 and Juniper Networks have released patches for two dozen critical-severity vulnerabilities, including bugs leading to RCE.
ENLer →
Microsoft: October Windows update may break Smart App Control
Microsoft says some users may have trouble turning on Smart App Control after installing this month's KB5127648 Windows 11 security update.
ENLer →
Microsoft Patches Two Dozen RCE Flaws in Office
Microsoft has rolled out fixes for over 30 vulnerabilities, including two dozen high-severity remote code execution bugs in Office.
ENLer →
BAE Systems cyberattack disrupts US federal court operations
The Administrative Office of the US Courts says a cyberattack on government contractor BAE Systems has taken down the notice system used by federal bankruptcy courts.
ENLer →
Proofpoint Inks $6.3 Billion All-Cash Deal to Acquire Varonis
The Thoma Bravo-owned Proofpoint will acquire Varonis in an all-cash transaction and Varonis will become a private company. The post Proofpoint Inks $6.3 Billion All-Cash Deal to Acquire Varonis appeared first on SecurityWeek .
ENLer →
China-Linked Hackers Exploited BeyondTrust Zero-Day to Take Over Remote Support Servers
The China-nexus cyber espionage group tracked as Armory Castle (previously UNC5221 or Warp Panda) exploited a newly disclosed security flaw in BeyondTrust Remote Support (formerly Bomgar) as a zero-day in late August 2026. The vulnerability, tracked as CVE-2026-102764 (CVSS score: 9.3), is a case of improper origin validation in an internal messaging component that could be exploited by a…
CVE-2026-102764ENLer →
CERT-In Warns AI Agents Accessed Sensitive Data at Indian Organizations During Testing
AI agents being tested online reached the live systems of Indian organizations and read business records, including personal data and confidential material, CERT-In said in an advisory on October 15. The agents went beyond their assigned tasks, and none of the organizations detected the unauthorized access. After internal reviews, the AI companies whose models were being tested…
ENLer →
BeyondTrust patches zero-day exploited in attacks since August
BeyondTrust warned customers on Thursday to patch a critical flaw in its Remote Support (RS) that has been exploited in zero-day attacks since late August.
ENLer →
PEERSTITCH Malware Deployed via FortiOS Flaw Bypasses Checks on Tagged VPN Sessions
A suspected advanced threat actor has been observed exploiting a security flaw in Fortinet FortiOS to deliver a previously unreported memory-resident ARM64 malware known as PEERSTITCH. The attack involves the exploitation of CVE-2025-61624 (CVSS score: 5.4), a path traversal flaw in the command line interpreter of FortiOS, FortiPAM, FortiProxy, and FortiSwitchManager that could allow a…
CVE-2025-61624ENLer →SecTor 2026 Reveals a Rapidly Shifting Cybersecurity Landscape
The event closed in Toronto last week, with experts sharing critical perspectives on emerging risks, drawing record attendance and marking 22% growth.
ENLer →F-Secure Launches Victim-First Scam Encyclopedia Covering 50+ Types of Consumer Fraud
Built from decades of threat intelligence research, the new resource explains scams from the victims' perspective and tracks emerging forms of cyber crime.
ENLer →
CISA alerta para exploração de zero-day no Ivanti
A CISA pediu que administradores corrijam appliances Ivanti Connect Secure após a exploração da CVE-2026-104935, falha zero-day que permite contornar autenticação remotamente e executar comandos, viabilizando roubo de credenciais e exfiltração de dados. O alerta foi publicado em 13 de outubro de 2026, quando a agência incluiu o problema em seu catálogo de vulnerabilidades conhecidas…
CVE-2026-104935Ler →
Falhas no Citrix XenServer ameaçam sistemas host
Administradores de ambientes virtualizados com XenServer 8.4 e XenServer 9 devem ficar atentos a quatro correções divulgadas pela Citrix. Três delas abrem caminho para que alguém já privilegiado dentro de uma máquina virtual afete o servidor que hospeda esse ambiente, seja comprometendo-o, seja provocando sua parada. A informação consta no boletim CTX697170, de 13 de…
Ler →
Proofpoint adquire Varonis por US$ 6,3 bilhões
A Proofpoint anunciou um acordo definitivo para adquirir a Varonis em uma transação em dinheiro avaliada em aproximadamente US$ 6,3 bilhões, embora o valor tivesse sido anunciado como US$ 5,9 bilhões no final do mês passado. A Varonis era uma das empresas do portfólio da Thoma Bravo, que adquiriu a empresa em 2015. No ano…
Ler →
Curl corrige falha de RCE encontrada pela Anthropic
Uma nova versão do Curl foi publicada com a correção de mais de vinte vulnerabilidades, incluindo uma falha de execução remota de código (RCE) encontrada pela empresa de inteligência artificial Anthropic. Apesar de permitir execução remota de código, o impacto da CVE-2026-92392 foi classificado como “alto”, e não crítico. Segundo o mantenedor do Curl, Daniel…
CVE-2026-92392Ler →
Agentes de IA ampliam riscos no setor bancário
A adoção de agentes de inteligência artificial capazes de consultar documentos, acessar aplicações, alcançar dados, usar credenciais, chamar APIs e executar tarefas exige que instituições financeiras ampliem controles de identidade, monitoramento e resposta a incidentes. Segundo a Pesquisa Febraban de Tecnologia Bancária 2026, os bancos pretendem investir cerca de R$ 3 bilhões em Inteligência Artificial,…
Ler →
AI Slop Isn't Just for Social Media; It's Ruining Cyberattacks, Too
Don't buy the hype! AI has been dumbing down cyberattacks, and serious threat actors are barely touching it.
ENLer →
Hackers exploit Collabora RCE flaw to backdoor Nextcloud servers
Threat actors are exploiting a critical command execution flaw, now tracked as CVE-2026-110447, in the Collabora Online - Built-in CODE Server app (richdocumentscode) for Nextcloud.
CVE-2026-110447ENLer →
Critical PwnEscape Linux Kernel Vulnerability Lets Guest VMs Read Host Memory
A newly disclosed critical flaw in the Linux kernel allows code inside a virtual machine to read memory on the host computer it runs on. A researcher demonstrated the leak against Vercel's live cloud sandboxes, and Vercel confirmed it. The flaw, now tracked as CVE-2026-99999 and nicknamed PwnEscape, is in the Linux kernel's networking code, not in any one cloud's setup, so it reaches the shared…
CVE-2026-99999ENLer →
Segurança cibernética depende de humanos bem preparados
Equipes bem treinadas são o pilar do sistema de segurança cibernética de qualquer empresa, mas muitos programas de conscientização se limitam a simulações periódicas de phishing por e-mail e treinamentos anuais de poucos minutos. Enquanto isso, criminosos desenvolvem abordagens cada vez mais sofisticadas para aplicar golpes por telefone, aplicativos de mensagem, redes sociais e conteúdos…
Ler →
Hackers sequestram D-Link e Ubiquiti para revender banda
Uma campanha de proxyjacking atingiu dispositivos em 34 países e monetizou conexões de internet das vítimas por meio de uma rede comercial de proxies residenciais. O operador instalou o Pawns.app, aplicativo legítimo de compartilhamento de banda que permite a usuários ganhar dinheiro cedendo suas conexões, nos aparelhos sem o consentimento dos donos. As informações são…
Ler →
Android gets AI defenses against messaging scams, fake calls
Google announced new AI-powered defenses against scam messages and call-forwarding abuse on Android, currently rolling out to eligible devices.
ENLer →
ThreatsDay: Adobe RCE, DNS Wallet Theft, NVIDIA Container Escape, Self-Healing Backdoor + 23 More
Someone built a tool to steal data, then decided it should scare the victim for fun. Yes, that’s an actual feature. And somehow, it fits right in with this week's security stories. The rest gets interesting in different ways. A small permission can lead to a big theft. A trusted login can hide the wrong person. Old bugs are finding new victims, familiar tools are being put to strange uses, and…
ENLer →
Hackers hijack D-Link, Ubiquiti devices to resell your stolen bandwidth
A proxyjacking campaign has impacted devices in 34 countries, monetizing victims' internet connections through a commercial residential proxy network.
ENLer →
Context Is King in the Fight Against Modern Cyberattacks
Contextual defense helps security teams connect the signals, anticipate what comes next, and stop threats before they escalate.
ENLer →
Fake Arch Linux packages push malware with root privileges
A threat actor uploaded malicious packages to the Arch User Repository (AUR) that impersonated two popular helper tools, yay and paru.
ENLer →
Watch Now: Zero Trust Strategies Summit – All Sessions Available on Demand
This summit is laser-focused on the next generation of Zero Trust and Identity security, moving beyond theory to deliver actionable strategies.
ENLer →
Citizen Lab Traces Zero-Click Candiru Spyware Infections at Al Jazeera to Targeted Online Ads
Candiru, an Israeli maker of spyware sold to governments, infected devices at the news network Al Jazeera through ordinary online ads, in attacks that needed no click or other action from the user, researchers at the Citizen Lab said Thursday. The hidden attack code ran the moment an ad loaded on the screen, and in some cases the ad loaded out of sight, in the background. The Citizen…
ENLer →
Silent Lynx Exploits WinRAR Flaw to Deploy Reverse Shell in CIS Government Attacks
The threat actor known as Silent Lynx has been attributed to a fresh set of attacks targeting government organizations across the Commonwealth of Independent States (CIS). The activity, observed from June 2025 through August 2026, involves four different infection chains that make use of macro-enabled documents, PS2EXE downloaders, GitHub-hosted PowerShell, and crafted WinRAR archives…
ENLer →
Vulnerability Management Isn't About the Score — It's About How It Applies to You
Organizations need to move away from vendor-assigned, theoretical scores toward real exploit data specific to their environments.
ENLer →
UK Legal Aid Agency Hack Scope Widens After Forensic Review
The UK’s Legal Aid Agency has confirmed that records dating back to 1978 were stolen in an April 2025 data breach.
ENLer →
Is AI pentesting as good as a human pentester?
AI pentesting can uncover vulnerabilities missed by human testers, but it also has limitations in consistency, risk assessment, and understanding business context. Intruder compares the strengths and weaknesses of both approaches and explains where AI agents can improve security testing.
ENLer →Eclipse Foundation Eclipse Milo
View CSAF Summary Successful exploitation of these vulnerabilities could allow an attacker to delete protected data, recover user credentials and impersonate legitimate users, or cause the server to stop responding to all clients.
CVE-2026-62927ENLer →